Recommended Free Tools
To give a script access to one Hugging Face repository, create a fine-grained user access token, select only that repository and the required action, and then verify that your account and organization can already access it. The token narrows your authority; it cannot bypass organization policy or gated-model approval. For CI/CD, a Trusted Publisher OIDC exchange is usually safer than storing a long-lived user token.
What a fine-grained token actually controls
A Hugging Face user access token is a credential representing a user account. Its effective authority is the intersection of three controls:
- Your account’s existing access: the repositories and actions you can use when signed in normally.
- Organization permissions: your role, Resource Group membership, and any organization token policy.
- The token’s role and resource scope: the operations and repositories selected when the token is created.
A fine-grained token can reduce what an application may do with your credential, but it does not elevate your account. If you cannot open a private repository in the web interface, a token scoped to that repository will not make it available. If a model repository is gated, the token does not replace the model’s request-and-approval process.
This distinction matters when the goal is “one repository only.” You must first make the repository reachable by the correct user or organization members, then issue a credential whose scope is no broader than the job requires.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall

- HD streaming made simple: With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- Compact without compromises: The sleek design of Roku Streaming Stick won’t block neighboring HDMI ports, and it even powers from your TV alone, plugging into the back and staying out of sight. No wall outlet, no extra cords, no clutter.
- No more juggling remotes: Power up your TV, adjust the volume, and control your Roku device with one remote. Use your voice to quickly search, play entertainment, and more.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
- TV, simplified: With setup that only takes minutes, a simple-to-navigate Home Screen, and an uncluttered remote control that does all you need—Roku makes it easier to watch the TV you love.
Choose the operation before creating the token
Start with the exact job the credential will perform. Downloading files, running inference, and pushing commits have different risk levels.
| Job | Minimum useful capability | Typical identity choice | What to avoid |
|---|---|---|---|
| Download files from one repository | Read access to that repository | Fine-grained read scope, or a read token if fine-grained selection is unavailable | Write access or a token covering every repository you can reach |
| Run an application or inference client | Read access to the model or dataset and any separately required service permission | Fine-grained read scope; for CI, an account Trusted Publisher identity when appropriate | Assuming the token grants access to a gated model that has not approved your account |
| Push commits, model artifacts, or dataset updates | Write permission on the target repository | Fine-grained write scope limited to the target repository, or a repository Trusted Publisher | Using an account-wide write token in an unattended job |
| Publish from CI without a persistent secret | Short-lived write permission for the configured repository | Trusted Publisher with the CI provider’s OIDC identity | Putting a long-lived user token in command arguments or build logs |
If the job performs more than one operation, list them separately. A download step may need only read access even when a later release step needs write access. Splitting those jobs lets you use different credentials and limits the consequences of a mistake.
Create a fine-grained token in Access Tokens
Hugging Face manages user tokens in your account settings under Access Tokens. The exact wording of controls can change, but the workflow is consistent: select a role, choose the narrowest permissions and resources, create the token once, and store it securely.
- Sign in as the account that will perform the job. Confirm that this account can open the target repository and carry out the intended operation without a token. This catches missing organization membership and gated-model approval before you create a credential.
- Open your account settings and choose Access Tokens. Create a new user access token rather than reusing a token issued for another application. Give it a descriptive name that identifies the workload, repository, and environment, such as
docs-build-read-private-model. - Select the fine-grained role. Fine-grained tokens are intended for production applications that should not inherit every resource available to a person. The permission editor should let you narrow access to selected resources and actions.
- Select the repository or organization resource. For a one-repository job, select only that repository. Do not select an entire organization or a broad “all repositories” option unless the application genuinely needs it. If the repository is owned by an organization, make sure the organization resource is the one being scoped.
- Choose actions deliberately. Select read permission for downloads and read-only inference clients. Add write permission only when the process must create or modify repository content. Do not add administrative capabilities for a build that only downloads files.
- Review the summary before creating the token. Check the account, repository, organization, and action list. A fine-grained token should describe one workload, not your complete personal access.
- Create the token and copy its value immediately. Treat the displayed value as a secret. Store it in the CI provider’s encrypted secret store or an approved secret manager. Do not paste it into a ticket, source file, notebook, image, or chat message.
- Record ownership and rotation information outside the token value. Note which service uses it, who owns that service, which repository it reaches, and when it should be reviewed. This makes revocation possible when a job is retired or an employee changes role.
The token editor may expose more detailed choices than your job needs. Prefer the smallest set of permissions and resources that lets the job complete. A successful creation only proves that the token was issued; it does not prove that organization policy will permit every requested resource at runtime.
Rank #2

- Ultra-speedy streaming: Roku Ultra is 30% faster than any other Roku player, delivering a lightning-fast interface and apps that launch in a snap.
- Cinematic streaming: This TV streaming device brings the movie theater to your living room with spectacular 4K, HDR10+, and Dolby Vision picture alongside immersive Dolby Atmos audio.
- The ultimate Roku remote: The rechargeable Roku Voice Remote Pro offers backlit buttons, hands-free voice controls, and a lost remote finder.
- No more fumbling in the dark: See what you’re pressing with backlit buttons.
- Say goodbye to batteries: Keep your remote powered for months on a single charge.
Verify the account and organization authorization boundary
Before troubleshooting the token, verify the account’s own authorization. Token scope is always bounded by it.
- For a personal private repository, confirm the account owns the repository or has been granted the required repository role.
- For an organization repository, confirm that the account is still a member and that its organization role includes the needed action.
- For a gated model, confirm that the account has submitted the required request and that the repository owner has approved it.
- For an organization with token controls, check whether an administrator must approve a fine-grained token before it can reach organization resources.
Organization roles include no_access, read, contributor, write, and admin. A no_access member cannot use organization repositories or settings through ordinary organization membership. A contributor has additional write rights on repositories that member created, while write grants write rights across organization repositories. A token cannot turn a read member into a write member.
Use Resource Groups to limit organization repository visibility
Fine-grained tokens limit a credential. Resource Groups limit which organization members can reach selected repositories. They solve different parts of least privilege and can be used together.
Resource Groups are available on Team and Enterprise plans. An organization administrator creates a group, assigns repositories to it, adds members, and gives each member a group role. Group roles are read, contributor, write, and admin.
Rank #3

- 4K streaming made simple:With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- 4K picture quality: With Roku Streaming Stick Plus, watch your favorites with brilliant 4K picture and vivid HDR color.
- Compact without compromises: Our sleek design won’t block neighboring HDMI ports, and it even powers from your TV alone, plugging into the back and staying out of sight. No wall outlet, no extra cords, no clutter.
- No more juggling remotes: Power up your TV, adjust the volume, and control your Roku device with one remote. Use your voice to quickly search, play entertainment, and more.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
- A private repository assigned to a Resource Group is visible only to members of that group.
- Public repositories remain visible to anyone, regardless of Resource Group membership.
- A repository belongs to only one Resource Group.
- A member may belong to several Resource Groups.
- The group role determines what that member can do with the repositories assigned to the group.
Administrator workflow
- Open the organization’s access-control area and create a Resource Group for a coherent set of repositories, such as the models used by one production service.
- Assign the private repository to that group. Because a repository can belong to only one group, choose the group that should own its access policy.
- Add only the organization members or service identities that need the repository.
- Assign each member the least powerful group role that supports the work. Use
readfor consumers,contributorfor limited authoring, andwriteoradminonly when their responsibilities require it. - Have each automation owner create a token after membership is configured, then scope that token to the repository and action required by the job.
This two-layer arrangement means a private repository is hidden from unrelated organization members, while an individual token still prevents an approved member’s application from accessing other repositories or writing when it only needs to read.
Account policies can require approval for fine-grained tokens
Team and Enterprise administrators can manage token access under organization policies. Depending on policy, an organization may require fine-grained tokens, require administrator approval, or otherwise control which tokens may access organization resources.
Consequently, a token can be created successfully and still fail when a job requests an organization repository. Ask an organization administrator to check the token policy and approval state. Do not “fix” an approval failure by switching to a broad write token; that bypasses the intended control and increases exposure.
Gated repositories need separate approval
Some model repositories are gated. The repository owner may require a user to request access and share contact information before downloading files. A read token authenticates the account, but it does not satisfy those repository-specific rules.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #4
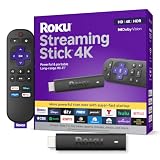
- Stunning 4K and Dolby Vision streaming made simple: With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- Breathtaking picture quality: Stunningly sharp 4K picture brings out rich detail in your entertainment with four times the resolution of HD. Watch as colors pop off your screen and enjoy lifelike clarity with Dolby Vision and HDR10+.
- Seamless streaming for any room: With Roku Streaming Stick 4K, watch your favorite entertainment on any TV in the house, even in rooms farther from your router thanks to the long-range Wi-Fi receiver.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
- Compact without compromises: Our sleek design won’t block neighboring HDMI ports, so you can switch from streaming to gaming with ease. Plus, it’s designed to stay hidden behind your TV, keeping wires neatly out of sight
For an organization-owned gated repository, the owner can require organization members to request access as well. The documented exceptions include organization administrators, the repository creator, and Resource Group administrators when the model belongs to a Resource Group. If your account is not covered by an exception, complete the request process first.
Diagnose a gated-model failure
- If the web page says access is pending, wait for the owner’s decision; changing token roles will not accelerate approval.
- If the account was approved but the job still fails, make sure the token belongs to that same account and is scoped to the correct repository.
- If an organization policy is involved, confirm that the organization allows the account and token to use the approved gated repository.
Prefer Trusted Publishers for CI/CD when supported
A long-lived user token is simple but creates a persistent secret that must be protected and rotated. Hugging Face Trusted Publishers let a configured CI provider exchange its OpenID Connect (OIDC) identity for a short-lived Hub token at job runtime.
The documented Trusted Publisher token lifetime is 60 minutes. The exchange gives the job a temporary credential instead of requiring the repository to store a permanent user token.
| Trusted Publisher configuration | Permission focus | Useful when |
|---|---|---|
| Repository publisher | Write access to one configured repository | A build or release workflow publishes artifacts to a specific repository |
| Account CI identity | Acts for the configured account; can read gated repositories that account already has access to | A workflow needs the account’s existing read access, with optional Inference Provider use when configured |
Set up the OIDC pattern
- Decide whether the workflow publishes to one repository or needs the account’s existing access to several approved resources. Choose the repository-publisher or account-identity model accordingly.
- In Hugging Face, configure the Trusted Publisher with the CI provider, repository, workflow or equivalent identity constraints required by that provider.
- In the CI workflow, enable OIDC permissions and request the exchange at runtime using the provider’s supported integration.
- Pass the resulting short-lived token to the Hugging Face client through the job environment or a temporary protected file.
- Check that the account or repository still has the required organization and gated-model permissions. OIDC proves the workflow identity; it does not grant access the associated account or repository lacks.
- Restrict which branches, tags, environments, or workflow identities can request the exchange, using the CI provider’s policy controls.
Use a persistent fine-grained token only when OIDC is unavailable or the workload genuinely requires a user-managed credential. Even then, keep its scope to the smallest repository and action set.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Best Value

- The Google TV Streamer (4K) delivers your favorite entertainment quickly, easily, and personalized to you[1,2]
- HDMI 2.1 cable required (sold separately)
- See movies and TV shows from all your services right from your home screen[2]; and find new things to watch with tailored recommendations for everyone in your home based on their interests and viewing habits
- Watch live TV and access over 800 free channels from Pluto TV, Tubi, and more[3]; if you find an interesting show or movie on your TV, mobile app, or Google search, you can easily add it to your watchlist, so it’s ready when you are[2]
- Up to 4K HDR with Dolby Vision delivers captivating, true-to-life detail[4]; and you can connect speakers that support Dolby Atmos for more immersive 3D sound
Handle token values without leaking them
Hugging Face’s operational guidance is explicit: “To avoid leaking token values in shell history or logs, pass them via environment variables or files, and avoid pasting raw tokens directly into command lines.”
For a local test, set the value in your shell environment through your operating system’s secret mechanism, then invoke the client without placing the token in the command itself. In CI, map the encrypted secret to an environment variable supplied only to the step that needs it. Masking should be enabled in the CI platform, but do not rely on masking alone: a token transformed, echoed, or embedded in an error message may still be exposed.
# The value is injected by the shell or CI secret manager.
export HF_TOKEN="$HF_TOKEN_SECRET"
python download_model.py
Do not commit the value to a repository, write it to a build artifact, include it in a URL, or print the complete environment. If a token appears in logs, history, a notebook, or source control, revoke it immediately and create a replacement with the same or narrower scope.
Test that the restriction is real
Testing should confirm both the intended operation and the denied operations. Use a disposable job or a safe read-only check where possible.
- Run the intended download, inference, or push against the selected repository.
- Attempt a harmless read of a different private repository that the account can normally access. The fine-grained token should not authorize it when that repository was not selected.
- If the token is read-only, verify that a write operation is rejected rather than silently succeeding.
- For an organization repository, test with the same organization policy and membership used by production; a personal test account may produce a misleading result.
- For a gated model, verify that the approved account can read it while an unapproved account cannot.
- Remove the test credential after validation and issue the production credential through the approved storage path.
Never test by modifying an important repository. A denied request is evidence that a boundary is working; it is not a reason to broaden the token immediately.
Troubleshoot common failures
| Symptom | Likely cause | Corrective action |
|---|---|---|
| Authentication fails immediately | The token is malformed, revoked, mapped to the wrong environment, or not being passed to the client. | Inject it again through the secret manager, check for accidental whitespace, and verify that the token belongs to the intended account. |
| Private repository returns not found or unauthorized | The account lacks repository access, the repository was omitted from the fine-grained scope, or an organization policy blocks the token. | Open the repository as the token’s account, confirm the selected resource, and ask an organization administrator to check approval and policy state. |
| Download of a gated model is denied | The account has not requested access, approval is pending, or the token represents a different account. | Complete the repository’s request process, wait for approval, and then use a token issued for the approved account. |
| Push is denied while downloads work | The token has read permission only, or the account has no write role on the repository. | Grant write authority to the account only if required, then create a separate fine-grained write token or use a repository Trusted Publisher. |
| Token creation succeeds but organization access fails | The organization requires administrator approval or has a policy restricting token access. | Have an administrator review the token under the organization’s token-management controls. |
| CI works for an hour and then stops | A Trusted Publisher token has reached its documented 60-minute lifetime. | Request a fresh OIDC exchange during each job instead of caching the token across runs. |
Rotate, revoke, and separate credentials
Give each production workload its own token or Trusted Publisher identity. Separate credentials make it possible to revoke one service without interrupting unrelated jobs and make audit records easier to interpret.
- Rotate a persistent token on a schedule set by your security policy and whenever its owner, repository, or workflow changes.
- Revoke immediately when a token may have appeared in a log, shell history, notebook, or source-control commit.
- Use read-only tokens for build and inference stages that do not publish.
- Use a different write credential for release automation, scoped to the repository that receives the release.
- Delete credentials for retired repositories, experiments, and former workflows.
- Review organization Resource Group membership and token approvals when a person changes teams or leaves the organization.
Do not make a credential broader merely to reduce the number of secrets. Fewer, well-scoped identities are safer than one all-purpose token shared by every job.
Quick Recap
A practical least-privilege checklist
- Have you named the exact repository, organization, and operation?
- Can the token’s account perform that operation interactively before automation is configured?
- Did you choose fine-grained scope instead of a broad write role?
- Is the repository private, in a Resource Group, or gated, and have those separate approvals been completed?
- Does an organization policy require administrator approval for the token?
- Would a Trusted Publisher provide a 60-minute credential instead of a persistent secret?
- Is the value injected through an environment variable or protected file rather than a command argument?
- Have you tested both the required action and an action that should be denied?
- Is there an owner and rotation or revocation plan for the credential?
Which approach should you use?
| Situation | Recommended control | Reason |
|---|---|---|
| A local tool needs read access to one private repository | Fine-grained read token scoped to that repository | Limits the credential without granting write access |
| An organization has several private repositories for separate teams | Resource Groups plus member-appropriate fine-grained tokens | Controls both repository visibility and application actions |
| A CI workflow publishes to one repository | Repository Trusted Publisher | Uses OIDC and a documented 60-minute token with repository-focused write access |
| A CI workflow reads gated models already approved for one account | Account Trusted Publisher, where supported | Uses a short-lived identity while preserving the account’s existing approvals |
| A job must use a persistent credential because OIDC is unavailable | Dedicated fine-grained token with the narrowest read or write scope | Provides a manageable fallback without exposing the user’s full access |
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →

Say something about this film