If a Hugging Face access token may have leaked, invalidate it immediately, then investigate activity and harden the account. For a token you own, open Settings > Access Tokens and use Manage to delete or refresh it. If the credential must be disabled everywhere, submit it to Hugging Face’s leaked-credential endpoint, POST /api/credentials/revoke. Organization administrators have a different control: they can remove a member token’s access to their organization, but that token may continue working for the owner’s other resources.
After containment, rotate related credentials, review account or organization activity, enable authenticator-app two-factor authentication (2FA), protect recovery codes, and remove copies of the token from local machines and CI/CD systems.
Contain the exposed token first
Investigation can wait; a credential that might be usable should not. Work through these steps in order and avoid copying the secret into chat, tickets, screenshots, shell history, or logs.
- Identify the credential. Determine which token was exposed, where it was stored, and which applications or machines use it. If you cannot prove that a suspicious value was harmless, treat it as exposed.
- Delete or refresh your own token. Sign in to Hugging Face, open Settings > Access Tokens, select Manage, and delete or refresh the affected token. The official user access token documentation describes this as the owner’s normal containment route.
- Use global revocation when the credential must stop everywhere. The leaked-credential endpoint invalidates a matching token immediately and does not require rights over the account or organization that owns it.
- Replace the credential in every dependent system. Update deployment secrets, notebooks, local environment variables, scheduled jobs, container definitions, and secret managers only after the old value has been invalidated.
- Record the incident safely. Note the approximate exposure time, affected repositories or systems, and actions taken, but store only a fingerprint or other non-secret identifier—not the raw token.
Deleting a token in the web settings and calling the global endpoint are both containment actions. Neither one tells you whether an attacker already used the credential, so activity review remains necessary.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →#1 Best Overall

- HD streaming made simple: With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- Compact without compromises: The sleek design of Roku Streaming Stick won’t block neighboring HDMI ports, and it even powers from your TV alone, plugging into the back and staying out of sight. No wall outlet, no extra cords, no clutter.
- No more juggling remotes: Power up your TV, adjust the volume, and control your Roku device with one remote. Use your voice to quickly search, play entertainment, and more.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
- TV, simplified: With setup that only takes minutes, a simple-to-navigate Home Screen, and an uncluttered remote control that does all you need—Roku makes it easier to watch the TV you love.
Choose the revocation route with the right scope
Hugging Face exposes two materially different controls. Select the one that matches the problem rather than assuming every revocation is account-wide.
| Route | Who can initiate it | What becomes unavailable | What may remain available | Use it when |
|---|---|---|---|---|
| Delete or refresh in Settings > Access Tokens | The token owner | The selected token is removed or replaced for that account | Other tokens and unrelated credentials are unaffected | Your own token is exposed, obsolete, or no longer needed |
POST /api/credentials/revoke |
Anyone who can safely submit the raw token value; account or organization ownership is not required | A matching submitted credential is invalidated everywhere | No service use of that matching token should continue | A leaked token needs global invalidation, including when ownership is unclear |
| Organization token revocation | An eligible organization administrator | The member token loses access to that organization permanently | The same token can continue working for the owner’s other resources | An organization needs to remove one member’s access without globally disabling the credential |
The organization-scoped behavior is documented in Hugging Face’s token-management guide. It is administrative access control, not a substitute for global invalidation of a leaked credential.
Delete or refresh a token from the Hugging Face settings
Use the web interface for a token you own
- Sign in to the affected Hugging Face account.
- Open Settings, then Access Tokens.
- Find the token associated with the exposed application, machine, or workflow.
- Choose Manage and delete or refresh the token.
- Issue a replacement with only the permissions that workflow requires.
- Update each legitimate consumer with the replacement, then test the application using the least privileged operation it needs.
Refreshing or deleting the token is preferable to leaving a credential active while you investigate. Keep the replacement out of source control and do not paste it into an issue, support request, or diagnostic transcript.
Use the global leaked-credential endpoint when necessary
The documented endpoint accepts multiple raw token values in a credentials array. A matching credential is invalidated immediately and stops working everywhere. The endpoint does not require permission over the account or organization that owns the token, which is important when a secret was found in a public repository or a shared log.
Keep the token in a protected environment variable or file. Do not place it directly in a command that your shell records. A request can be constructed with a variable named HF_EXPOSED_TOKEN and sent to the endpoint:
printf '%s' '{"credentials":["'"$HF_EXPOSED_TOKEN"'"]}' | curl --request POST 'https://huggingface.co/api/credentials/revoke' --header 'Content-Type: application/json' --data-binary @-Before running a command like this, check your shell history and process-monitoring policy. Some environments expose command arguments to other users, and shell history may retain the full line. A safer pattern is to create the request body from a protected file or use a secret-aware HTTP client that does not log payloads. Never replace the variable with a real token in documentation or a screenshot.
Submit several exposed credentials in one request
If an application used more than one Hugging Face token, include each raw value in the same credentials array. Keep the values in a protected file or secret manager and destroy temporary files after the request. If you cannot safely handle the values, use the web settings for tokens you own and contact Hugging Face support or security personnel for the remaining case.
Rank #2

- Ultra-speedy streaming: Roku Ultra is 30% faster than any other Roku player, delivering a lightning-fast interface and apps that launch in a snap.
- Cinematic streaming: This TV streaming device brings the movie theater to your living room with spectacular 4K, HDR10+, and Dolby Vision picture alongside immersive Dolby Atmos audio.
- The ultimate Roku remote: The rechargeable Roku Voice Remote Pro offers backlit buttons, hands-free voice controls, and a lost remote finder.
- No more fumbling in the dark: See what you’re pressing with backlit buttons.
- Say goodbye to batteries: Keep your remote powered for months on a single charge.
Understand the endpoint’s 202 response
Hugging Face states that the endpoint always returns 202 Accepted, whether or not any submitted token existed. A successful HTTP response therefore does not confirm that your value matched an active credential, nor does it prove that the token was used.
Recommended Free Tools
Use the response only as confirmation that Hugging Face accepted the revocation request for processing. Do not retry repeatedly as a way to test validity; repeating the same request is harmless according to the documentation, but it cannot reveal whether the original value was real.
After submission:
- Expect the matching token owner to receive an email notification.
- Create a new token to restore legitimate access; the revoked credential itself cannot be reactivated.
- Replace the old value in every service and machine that used it.
- Test with the new credential and monitor for authentication failures that identify a forgotten dependency.
These semantics are specified in the user access token documentation, including the warning that 202 Accepted is not proof that a submitted credential existed.
Do not confuse organization revocation with global invalidation
On Enterprise and above, an organization administrator can revoke a member token’s access to that organization. Hugging Face describes this action as permanent for the organization and provides no un-revoke operation. The token can nevertheless continue to access resources belonging to its owner elsewhere.
That distinction changes the response:
- If the concern is that a departing member should no longer reach one organization, use the organization administrator’s revocation control and then remove the member or adjust their role as appropriate.
- If the raw token appeared in a public location, a compromised workstation, or an attacker’s possession, use the global leaked-credential endpoint or delete the token from its owner account. Organization-only revocation leaves the credential usable outside that organization.
- If both conditions apply, perform the global invalidation first, then use organization controls to document and contain the member-access event.
Do not tell an affected token owner that organization revocation has disabled the credential everywhere. It has not. The scope and permanence are explained in Tokens Management.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteReview activity and rotate related credentials
Revocation stops future use of the affected token; it does not erase evidence of earlier use. Review recent account activity, repository changes, automated jobs, and cloud or secret-manager logs for actions you do not recognize.
In its July 2026 security incident disclosure, Hugging Face reported analyzing an attacker action log containing more than 17,000 recorded events. That figure describes the published incident analysis, not the number of affected accounts and not a prediction about your account. The same disclosure advises, as a precaution, rotating access tokens and reviewing recent activity. Read the official July 2026 incident disclosure for the incident-specific guidance.
Rank #3

- 4K streaming made simple:With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- 4K picture quality: With Roku Streaming Stick Plus, watch your favorites with brilliant 4K picture and vivid HDR color.
- Compact without compromises: Our sleek design won’t block neighboring HDMI ports, and it even powers from your TV alone, plugging into the back and staying out of sight. No wall outlet, no extra cords, no clutter.
- No more juggling remotes: Power up your TV, adjust the volume, and control your Roku device with one remote. Use your voice to quickly search, play entertainment, and more.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
What to look for in an account review
- New tokens, changed token names, or unexpected permission changes.
- Repository commits, pull requests, settings changes, or releases that you did not make.
- Unexpected downloads, uploads, model or dataset changes, or automation runs.
- New organization memberships, role changes, invitations, or removed collaborators.
- Authentication failures or successful logins from times and locations inconsistent with your normal use.
Rotate any other credential that was stored beside the exposed token or could have been read by the same process: cloud keys, package-registry credentials, database passwords, signing keys, and CI secrets. Rotating only the Hugging Face token is insufficient if the attacker also accessed the machine, repository, or secret store containing it.
If you believe the July 2026 incident affected you or you need to report a security concern, the disclosure directs users to [email protected]. Treat that address as an incident-reporting channel, not as evidence that every account was compromised.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Clear out junk files and repair common Windows errors3Fix the driver behind crashes, sound loss and screen glitchesUse secret scanning correctly
Hugging Face runs TruffleHog on each push and sends notifications for verified secrets, as described in its Secrets Scanning documentation. A result marked “unverified” is not an all-clear: verification can fail for technical reasons even when a credential is valid or dangerous.
If a token appears in a repository or push:
- Revoke or refresh it immediately using the appropriate route.
- Remove the secret from the current branch and from any generated artifacts that will be distributed.
- Rewrite repository history only after containment, using a process your team understands; history rewriting does not invalidate the old credential by itself.
- Search forks, caches, build logs, issue attachments, notebook outputs, container layers, and local clones.
- Replace the value with a secret-manager reference and add a pre-commit or CI check that blocks future token-shaped secrets.
Do not wait for a scanner to verify the value before revoking it. The scanner’s job is detection; token invalidation is your containment control.
Enable authenticator-app 2FA and protect recovery codes
Hugging Face’s documented personal-account 2FA flow uses a six-digit one-time password (OTP) generated by an authenticator application. The guide lists Authy, Google Authenticator, Microsoft Authenticator, and FreeOTP as examples. It does not establish a physical security key as part of this OTP procedure.
- Open the account’s security settings and start the 2FA setup.
- Scan the displayed QR code or enter its setup secret into your authenticator application.
- Enter the current six-digit OTP to confirm enrollment.
- Save the generated recovery codes in a secure location before signing out.
- Test one recovery path while you still have normal account access, without consuming every code.
Each recovery code is single-use. Regenerating the recovery-code set invalidates the previous set, so replace old copies wherever they were stored and update your emergency-access procedure. Keep the codes separate from the password and from the device that normally generates OTPs.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →If you forget the password and lose access to 2FA, Hugging Face directs you to [email protected]. The documented recovery process requires identity verification with a recovery factor such as an SSH key or personal access token. Keep at least one supported recovery factor available before an incident occurs. See the official 2FA guide for the current setup and recovery instructions.
Rank #4
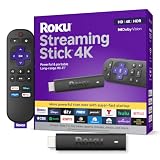
- Stunning 4K and Dolby Vision streaming made simple: With America’s number 1 TV streaming platform,* exploring popular apps—plus tons of free movies, shows, and live TV—is as easy as it is fun. *Based on hours streamed—Hypothesis Group
- Breathtaking picture quality: Stunningly sharp 4K picture brings out rich detail in your entertainment with four times the resolution of HD. Watch as colors pop off your screen and enjoy lifelike clarity with Dolby Vision and HDR10+.
- Seamless streaming for any room: With Roku Streaming Stick 4K, watch your favorite entertainment on any TV in the house, even in rooms farther from your router thanks to the long-range Wi-Fi receiver.
- Shows on the go: Take your TV to-go when traveling—without needing to log into someone else’s device.
- Compact without compromises: Our sleek design won’t block neighboring HDMI ports, so you can switch from streaming to gaming with ease. Plus, it’s designed to stay hidden behind your TV, keeping wires neatly out of sight
Clean up local CLI credentials and environment variables
Revoking a token on Hugging Face does not remove copies stored on your computers. The Hugging Face CLI command hf auth logout removes tokens stored locally by the CLI. It does not unset an HF_TOKEN environment variable, so that variable must be removed from the shell profile, operating-system secret store, CI configuration, container definition, or orchestration platform where it was set.
- Run
hf auth logouton each machine that used the old token. - Search shell profiles, service files, notebooks, task schedulers, Docker or image-build files, and CI variables for
HF_TOKENand the old token value. - Delete the old value from the relevant secret manager and replace it with the newly issued credential.
- Restart long-running services so they do not retain the old value in memory.
- Check logs and crash dumps for accidental disclosure, then restrict access to any retained incident evidence.
CLI logout is local credential cleanup. It is not evidence that browser sessions elsewhere have ended, and it does not revoke a token unless you separately delete or invalidate that token on Hugging Face.
The command behavior is documented in the Hugging Face CLI guide.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Use organization audit logs when the incident involves a team
Eligible Team and Enterprise organizations can inspect or export audit logs. Entries include the actor, action type and description, anonymized IP or location, and date and time. The documented event coverage includes security settings, token operations, membership, repository settings, and repository secrets or variables.
Open the organization’s audit-log interface, choose a time window that begins before the suspected exposure, and export the relevant entries for controlled analysis. Correlate token events with repository changes, membership changes, and your CI provider’s logs. Preserve the exported file with restricted access because even anonymized location and timestamps can be sensitive in a small team.
Hugging Face notes an important date boundary: granular organization-setting events are available only for actions after June 16, 2026. Older setting changes may appear under the broader org.update_settings event. Absence of a granular older event is therefore not proof that no setting changed.
Audit-log availability and event coverage depend on the organization plan and the event date. Consult the current Audit Logs documentation before treating an empty result as evidence that nothing happened.
Best Value

- The Google TV Streamer (4K) delivers your favorite entertainment quickly, easily, and personalized to you[1,2]
- HDMI 2.1 cable required (sold separately)
- See movies and TV shows from all your services right from your home screen[2]; and find new things to watch with tailored recommendations for everyone in your home based on their interests and viewing habits
- Watch live TV and access over 800 free channels from Pluto TV, Tubi, and more[3]; if you find an interesting show or movie on your TV, mobile app, or Google search, you can easily add it to your watchlist, so it’s ready when you are[2]
- Up to 4K HDR with Dolby Vision delivers captivating, true-to-life detail[4]; and you can connect speakers that support Dolby Atmos for more immersive 3D sound
Prevent the next token leak
Give every application its own token
Hugging Face recommends one token per application or use. A dedicated token lets you invalidate one workflow without breaking unrelated notebooks, deployments, or research jobs. Name tokens by purpose and owner, not by the secret value, and keep an inventory with creation date, permissions, consumers, and planned review date.
Prefer fine-grained production tokens
Use fine-grained tokens for production workloads so a leak exposes only the repositories or operations required by that workload. Start with read-only access where possible, add write or administrative permissions only when a documented task needs them, and remove obsolete permissions during each rotation.
Use short-lived identity for supported CI/CD workflows
For supported CI/CD systems, Hugging Face Trusted Publishers use the CI provider’s OIDC identity to obtain a short-lived Hub token. This avoids storing a long-lived Hub token as a CI secret. Confirm that your provider and workflow are supported, restrict the workflow identity to the intended repository and branch, and review the resulting permissions.
Build rotation into operations
- Set an owner and expiry review for every token.
- Store secrets only in an approved secret manager or protected environment variable.
- Block secrets in commits, notebook outputs, build artifacts, and logs.
- Require review for token creation and permission increases.
- Test emergency replacement procedures before a production incident.
- Delete tokens that belong to retired applications, contractors, or machines.
These practices align with Hugging Face’s token-security recommendations in the access-token documentation.
Troubleshooting and decision points
The endpoint returned 202, but I do not know whether the token was real
That is expected. The endpoint intentionally returns 202 Accepted whether or not a submitted value matched. Treat the token as unsafe, replace it wherever it was used, and use activity logs to investigate possible use.
An organization administrator revoked my token, but it still works elsewhere
That is the documented scope. Organization revocation removes access to that organization only. The token owner must delete or refresh the credential, or an authorized party must submit it to the global leaked-credential endpoint, to disable it everywhere.
The CLI logout command did not stop authentication
Check for HF_TOKEN in the environment. hf auth logout removes locally stored CLI tokens but does not unset that variable. Remove it from the machine or service configuration, restart the process, and verify that the old token has also been invalidated on Hugging Face.
Secret scanning says the value is unverified
Do not interpret that status as safe. Hugging Face explains that verification can fail for technical reasons. Revoke the suspected credential and investigate its source before deciding that it was harmless.
I lost both my password and my 2FA device
Use Hugging Face’s documented support route at [email protected]. Be prepared to verify identity with a recovery factor such as an SSH key or personal access token. Recovery codes cannot be reused, and regenerating them invalidates the previous set.
What a complete response looks like
A sound response has four separate records: the token was invalidated with the correct scope; every legitimate consumer received a replacement; account or organization activity was reviewed for the exposure window; and stronger authentication, least-privilege permissions, and recovery access were put in place. Keeping those records separate prevents a local logout, an organization-only restriction, or an ambiguous 202 response from being mistaken for proof that the entire incident is resolved.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.


Say something about this film